New Employee IT Onboarding Checklist: Accounts, Devices and Access (2026)
A step-by-step IT onboarding checklist for small businesses: accounts, devices, MFA and access in the first week, plus same-day offboarding.
A new hire’s first morning usually goes one of two ways. In the good version, they sit down at a prepared laptop, sign in with their own account, and are doing real work before lunch.
Table Of Content
In the bad version, someone is still hunting for a spare charger at noon, the new starter is borrowing a colleague’s login “just for today,” and their access gets sorted out sometime next week, maybe.
That second version is not just an inconvenience. It is a security decision made by default. Every shortcut taken on day one, a shared login, a personal email address used for work tools, an account copied from the last person in the role, tends to stay in place long after the first week.
Attackers know this. A login created in a hurry, with no second verification step and access to everything, is exactly the kind of account that gets found and abused months later.
The fix is not expensive software. It is a repeatable process: a short list of tasks done before the person arrives, a focused routine on day one, and a review at the end of the first week. This IT onboarding checklist walks through all three stages for a small business, in the order they should happen.
Before Day One: The Pre-Arrival Checklist
Most onboarding problems are created before the new employee ever walks in. These five tasks take a couple of hours in total, spread over the days between the signed offer and the start date.
Create a named account on the company domain
Set up the person’s own account on your business platform, Microsoft 365 or Google Workspace, using their real name and your company domain. Never let work start on a personal Gmail or Outlook address, and never hand over an account that belonged to a previous employee with the password changed.
A named account means every file, email and login can be traced to one person, and when that person eventually leaves, there is exactly one account to close.
Agree on a standard address format (firstname.lastname@, for example) and use it every time. Consistency sounds dull, but it is what makes the account list auditable at a glance.
Assign the license the role actually needs
Not every seat needs the most expensive plan. A warehouse supervisor, a bookkeeper and a designer use very different toolsets. Match the license to the job, note which extra apps the role requires, accounting, design, your CRM, and create those accounts now too, under the same named identity.
Write each one down as you create it. That written list becomes the backbone of your offboarding list later, and it is far easier to build it today than to reconstruct it on someone’s last day.
Prepare a company-owned device
Issue a company-owned laptop or desktop, not the employee’s personal machine. Before handover: install updates, turn on disk encryption, make sure endpoint protection is running, and enrol the device in whatever management tool you use so it can be locked or wiped if it is lost.
Record the serial number against the employee’s name in a simple asset list. Sign in once yourself to confirm everything works, a device that fails its first login burns the whole first morning.
Enrol MFA before the first morning
Do not leave multi-factor authentication as a task the new hire will “get around to.” Either enrol it with them on a short call before day one, or make it the very first job when they arrive, before email, before any other tool.
Federal CISA guidance for small businesses treats MFA on every account as a baseline, not an upgrade, and onboarding is the one moment when setting it up is expected rather than resisted.
Our separate guide to multi-factor authentication for small businesses compares the methods themselves; for onboarding purposes, the rule is simpler: no account is finished until its second step is switched on and tested.
Set access by role, not by copying someone
Decide what this job needs to reach and grant that, through role-based groups where your platform supports them, rather than cloning the access of whoever did the job before. The person who left may have accumulated years of extra permissions, and copying their account copies all of it.
Start narrow. Adding a folder later takes two minutes; discovering six months from now that a junior hire could open the payroll drive is a much worse conversation.
Day One: The 45-Minute Routine
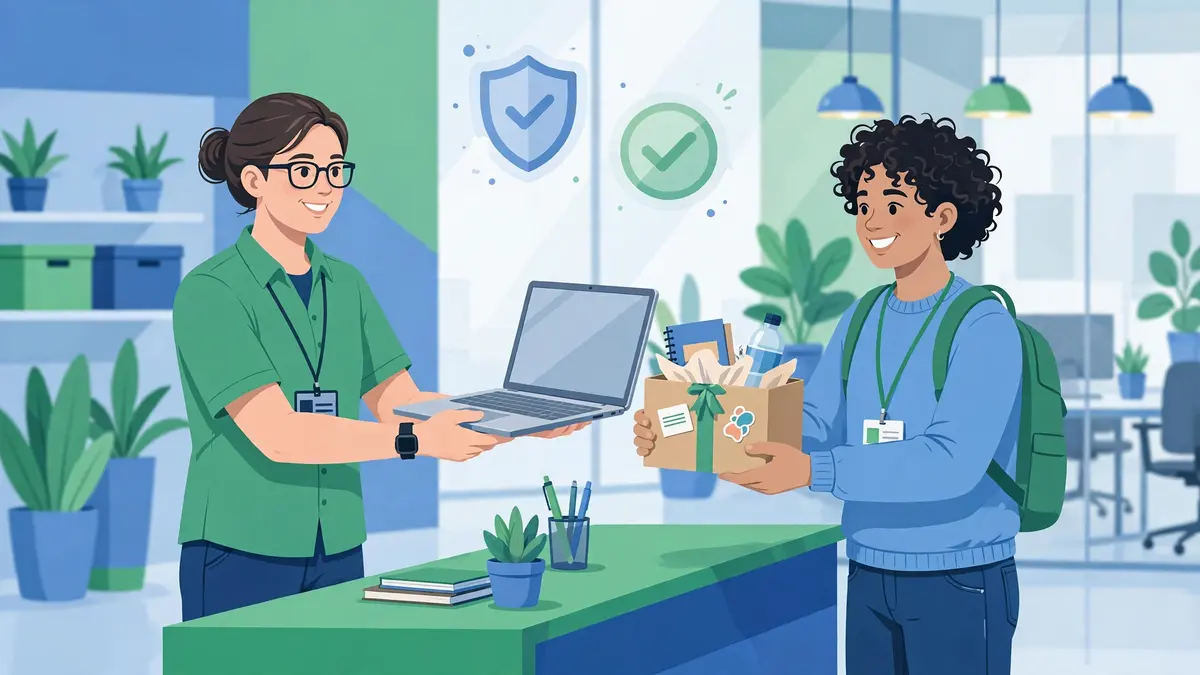
With the pre-arrival work done, day one is a guided session, not a scramble. Sit with the new hire, in person or on a call, and work through these steps together.
- Sign in and set their own password (10 minutes). They change the temporary password themselves, to a long passphrase only they know. Nobody else should ever know it, including you.
- Confirm MFA works (5 minutes). Have them sign out and back in so the second step is proven, not assumed. Save the recovery codes wherever your team stores them, not in a phone photo.
- Store credentials in the team vault (10 minutes). Add their work logins to the company password manager and show them the shared folders their role uses. If your team has not chosen one yet, our comparison of the best password manager for small business teams can roll out covers the realistic options at small-team prices. The point today is the habit: credentials live in the vault, never in chat messages or notebooks.
- Walk the shared drives (10 minutes). Open the exact folders and tools their role uses, and just as importantly, show them where things are not, who to ask when they need access to something new. That one conversation prevents most “can you just share your login?” requests.
- Cover the three house rules (10 minutes). Lock your screen when you step away. Never approve a sign-in prompt you did not trigger. Send anything that looks like a suspicious email to the named person who handles security questions. Keep it to three rules on day one; the fuller training comes during the week.
End the session by booking two things in the calendar: a 30-day access check, and the person’s first security training slot.
The First Week: Settle, Review, Train
Onboarding is not finished when the laptop works. The first week is where the setup gets tested against the real job.
Review access against reality. Around day five, compare what the new hire can reach with what the job has actually required. Remove anything granted “just in case” that turned out to be unnecessary, and add anything genuinely missing through the normal request route, not by sharing someone else’s account.
Run the first security training. A short, practical session beats a long policy document: how to spot a phishing email, how your team reports one, and what to do in the first five minutes if they think they clicked something bad.
Our guide to cybersecurity training for employees on a small budget covers how to build that into an ongoing routine; during onboarding week, one focused session is enough to set expectations.
Confirm the shared drives and tools are actually being used. Watch for workarounds: files appearing in personal cloud storage, or a team quietly running a project from one person’s account because it was “already set up.” Workarounds are a signal that the access design missed something, fix the design rather than scolding the person.
The Copy-Ready IT Onboarding Checklist
Copy this table into whatever tool your team already uses. One row per hire, ticked off as you go.
| When | Task | Done |
|---|---|---|
| Before day one | Named account created on the company domain | ☐ |
| Before day one | License and role-specific app accounts assigned and listed | ☐ |
| Before day one | Company device updated, encrypted, protected and recorded | ☐ |
| Before day one | MFA enrolment arranged (pre-start call or first task on arrival) | ☐ |
| Before day one | Role-based group access set, not copied from a previous employee | ☐ |
| Day one | Employee sets their own password; temporary password retired | ☐ |
| Day one | MFA tested with a real sign-out and sign-in | ☐ |
| Day one | Logins stored in the team password manager | ☐ |
| Day one | Shared drives walked through; access contact named | ☐ |
| Day one | Three house rules explained; 30-day access check booked | ☐ |
| First week | Access reviewed against the real job; extras removed | ☐ |
| First week | First security training session completed | ☐ |
| First week | No personal accounts or shared logins in use | ☐ |
| Last day (offboarding) | Every item on the account list closed or transferred | ☐ |
Offboarding: The Same List, in Reverse, on the Same Day
Everything above has a mirror image, and it must happen on the day someone leaves, not at the end of the week, not when IT gets around to it.
Work down the account list you created during onboarding: disable the main account first (this usually cuts off email and single sign-on in one move), then close or transfer each app account, remove them from shared folders and groups, rotate any shared credentials they knew, and recover the device.
Speed matters because an ex-employee’s still-active login is one of the most common findings when a small business later reviews who can reach its data.
It is also one of the first things insurers and clients ask about, which is why a documented joiner-and-leaver routine supports the picture you present when arranging cyber insurance for small business cover. The routine does not need to be complicated, it needs to be written down, owned by a named person, and done the same day.
Common Onboarding Mistakes
Shared logins. A single “office@” or “sales@” account that five people use feels efficient and is quietly dangerous: you cannot tell who did what, and you cannot remove one person’s access without changing the password for everyone. Give each person their own sign-in to the shared mailbox instead, every major platform supports delegated access.
Recycled accounts. Reusing a departed employee’s account for their replacement carries over their files, their permissions and their mistakes, and blurs accountability from the first day. Always create a fresh account; archive the old one.
Sticky-note passwords. A temporary password written on paper and handed over tends to stay written somewhere. Send it through your password manager’s sharing feature or read it out on a call, and force a change at first sign-in so it stops existing.
Access granted “temporarily” and forgotten. Day-one extras are rarely reviewed. That is exactly what the 30-day access check is for, put it in the calendar while you are still sitting with the new hire.
Treating setup as the finish line. The businesses that get caught out are usually not the ones with no process; they are the ones whose process ends at the laptop handover. The first-week review and the same-day offboarding are part of the same checklist, not optional extras.
Frequently Asked Questions
How long should new employee IT onboarding take?
The hands-on work is roughly two hours before the start date and about 45 minutes together on day one, followed by a short review inside the first week. Most of that time is waiting-free if the account and device are prepared in advance, the delays small businesses experience almost always come from starting setup on the morning itself.
What does a new employee need on their first day?
Four things: a named account on the company domain, a prepared company-owned device, MFA enrolled and tested, and access to only the tools and folders their role uses. If those four are in place, everything else, training, introductions, deeper permissions, can happen calmly during the first week.
Should new hires use their personal email for work tools?
No. Work accounts should sit on the company domain under the person’s own name. Personal email cannot be centrally secured, cannot be properly closed when someone leaves, and often breaches client or insurer expectations. If a tool needs an email address, it gets the work address.
Who should own the onboarding checklist in a small business?
One named person, the office manager, an IT lead, or the owner in very small teams. It does not need to be a technical specialist; it needs to be the same person every time, working from the same list, so nothing depends on memory. In a business with an outside IT provider, that person is the one who triggers the provider before the start date.
What happens if we skip the 30-day access review?
Temporary access becomes permanent access. Permissions granted in the first week are guesses; the review is the only step that compares them with the real job. Skipping it is how long-serving employees end up able to open systems nobody remembers giving them, and how a leaver’s forgotten access survives an offboarding that looked complete.
The Short Version
IT onboarding is a small process with an outsized effect. A named account, a prepared device, MFA switched on before the first morning, access matched to the role, a review at 30 days, and the same list run backwards on the day someone leaves, none of that needs new software or a security team.
It needs a written checklist and the discipline to use it for every single hire. Print the table above, name the person who owns it, and the next new starter’s first day takes care of itself.
No Comment! Be the first one.