How MSPs Can Help Small Business Clients Pass Cyber Insurance Audits and Renew Coverage
Cyber insurance audits now decide whether your clients get coverage, pay higher premiums, or get denied. Here is how an MSP can turn audit prep into a repeatable service that protects client renewals...
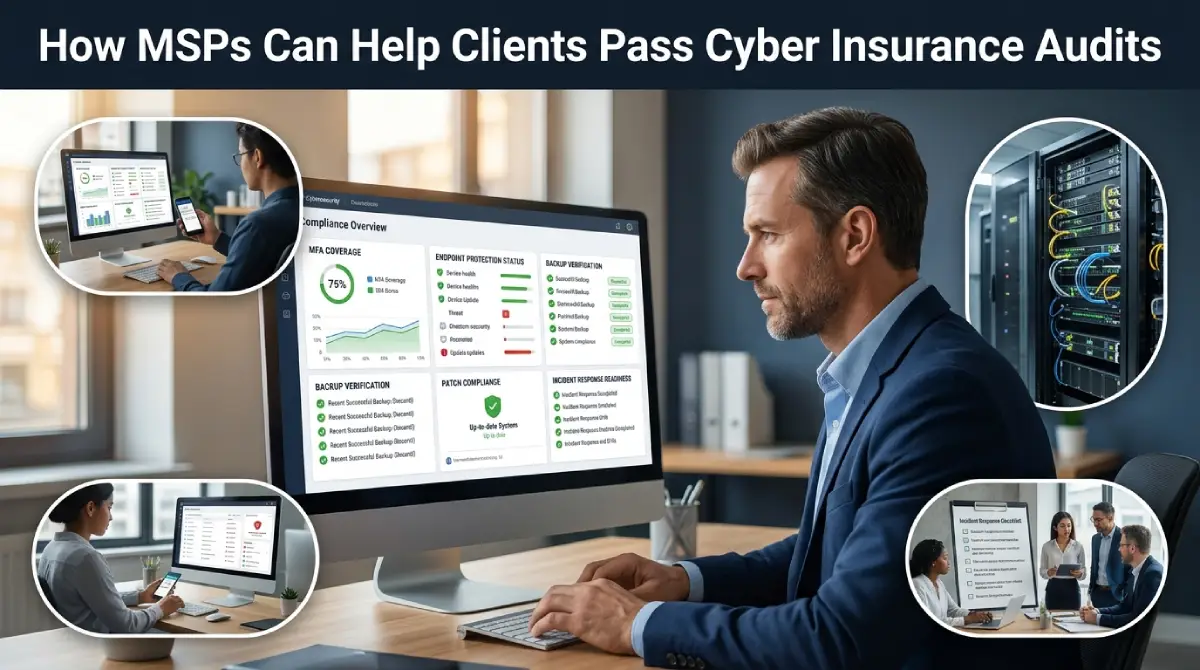
Wondering how to help MSP clients pass cyber insurance audits? Prove the controls; don’t just install them. Underwriters want evidence that MFA, endpoint detection, tested backups, and an incident response plan work across every user and device. The MSPs that win build one repeatable evidence process and run it before every renewal.
Table Of Content
- Why Cyber Insurance Audits Landed on the MSP’s Desk
- Step 1: Run a Client Risk Assessment Before the Questionnaire Arrives
- Step 2: Close the Control Gaps Insurers Weigh Most
- Step 3: Build an Evidence Pack Instead of a Folder of Screenshots
- Step 4: Write and Rehearse the Incident Response Plan
- Step 5: Fill In the Questionnaire Together, and Honestly
- Step 6: Keep Proving It All Year
- What to Do When a Client Cannot Pass Yet
- Turning Audit Readiness Into a Service That Pays
- Frequently Asked Questions
- Make Your Next Renewal Season the Calm One
That approach protects more than the client. A failed audit can mean a denied claim, a sudden premium jump, or an angry client pointing at you. Done well, audit readiness becomes a recurring service that lifts retention and supports a higher monthly rate. Here are the steps, the evidence insurers ask for, and the business case.
Why Cyber Insurance Audits Landed on the MSP’s Desk
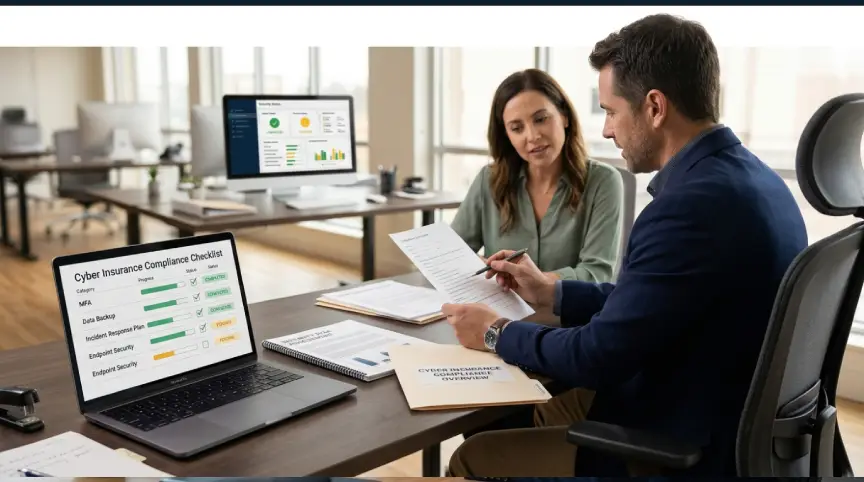
Not long ago, a small business ticked a few boxes on a renewal form and moved on. Now carriers ask for proof, and the person holding that proof is usually the managed service provider. The owner can’t explain a conditional access policy, so the questionnaire gets forwarded to you. That is the moment audit readiness stops being a favor and becomes part of the service.
The stakes are real on both sides. A misanswered question can void coverage right when a ransomware claim lands. For you, that can mean a lost account, a tense call with the client’s lawyer, or a weekend of unpaid cleanup. Insurers price risk on what they can verify, so open gaps show up in premiums. Fixing that is a business decision, not a technical chore.
Step 1: Run a Client Risk Assessment Before the Questionnaire Arrives
Start about 90 days before renewal. That gives you time to fix problems without rushed projects or panic pricing. Build a plain inventory first: users, devices, cloud apps, admin accounts, and where backups actually live. Real environments rarely match the last spreadsheet.
Then score the client against what carriers typically ask. Look hardest at MFA coverage, endpoint protection, backup quality, patch status, and anything running on unsupported software. End the review with a one-page gap list. Each gap gets a plain-language risk note and a rough cost to fix. Owners respond to that format because it ties spending to a premium or a claim outcome.
Step 2: Close the Control Gaps Insurers Weigh Most
Most questionnaires circle the same handful of controls. Treat the table below as a working cyber insurance audit checklist. It shows what underwriters usually want to hear and what proof you should produce on demand.
| Control | What the insurer usually asks | Evidence to keep |
|---|---|---|
| MFA | Enforced on email, remote access, and admin accounts | Policy export and enrollment report |
| Endpoint detection and response | Installed on all servers and workstations, and monitored | Console coverage report matched to device inventory |
| Backups | Offline or immutable copies, with restores tested | Dated restore test result |
| Patching | Critical updates applied within a set window | Patch compliance report |
| Email security | Filtering and phishing protection in place | Filter settings and phishing test results |
| Privileged access | Limited admin rights and separate admin accounts | Approved admin account list |
| Incident response plan | Written, with named roles, and tested | Plan document and exercise notes |
| Training | Regular security awareness for staff | Completion records |
A few patterns trip up clients again and again. MFA is switched on for email but skipped for service accounts, legacy protocols, or the one executive who complained. Endpoint detection is installed, yet nobody watches the alerts. Backups exist, but no one has restored from them in a year. Each of these is a quick fix when you catch it early. For deeper context on access design, our zero trust guide for small businesses explains the logic in plain terms.
Step 3: Build an Evidence Pack Instead of a Folder of Screenshots
A screenshot taken in a hurry proves very little. Brokers and carriers often want dated exports that show a control is live across the whole environment. Pull those reports straight from your RMM, identity platform, and security console. Store them in one folder per client, per renewal, and refresh them every quarter.
A solid evidence pack usually holds:
- A current asset inventory matched against endpoint agent counts
- MFA enrollment and conditional access policy exports
- The latest patch compliance report
- A dated backup restore test result
- The written incident response plan and last exercise notes
- Security awareness training completion records
Once this exists, a renewal becomes a copy-and-review job instead of a scramble. It also gives you a defensible record if a claim is questioned later.
Step 4: Write and Rehearse the Incident Response Plan
Plenty of clients say they have an incident response plan. Ask to see it, and you get a half-finished document from three years ago. Insurers notice that gap quickly. A usable plan names who decides, who calls the carrier, who restores systems, and in what order. Many policies expect fast notice of an incident, so the carrier hotline belongs on page one.
Keep the plan short enough that people will open it during a bad night. Then run a one-hour tabletop exercise once a year and record what you learned. That record counts as evidence, and it also shortens real downtime. If you need a starting point, our incident response plan guide for small businesses covers the basics without the jargon.
Step 5: Fill In the Questionnaire Together, and Honestly
Never let anyone answer yes to a control that is only planned. Misrepresentation on an application can lead to a denied claim or a rescinded policy, and that outcome lands on everyone’s desk. Sit down with the owner and go through each question line by line. Mark every answer as verified, partially in place, or not in place, and attach the matching evidence.
Have the owner sign off on the final answers, and keep a copy of what was submitted. If a question is ambiguous, ask the broker rather than guessing. Brokers handle this daily and often know how a specific carrier reads a phrase. This step costs an hour or two and can save the whole policy.
Step 6: Keep Proving It All Year
Audit readiness that exists only in renewal month will fall apart by spring. Add a short compliance view to your quarterly business reviews. Flag drift early, such as a new MFA exemption, a server missing patches, or a backup job that quietly failed. Refresh the evidence pack after any big change, like a new cloud platform or a wave of staff turnover. Clients see this as steady care, and you see fewer fire drills.
What to Do When a Client Cannot Pass Yet
It happens. A client may run unsupported servers or refuse to roll out MFA to every user. Don’t hide the problem. Sort the gaps by risk reduction per dollar, which usually points to MFA, backups, and endpoint detection first. Put the rest on a dated remediation plan the owner approves in writing.
Then talk to the broker early. Some carriers accept a documented plan with firm deadlines, while others may price higher or decline. Either way, the client decides with full information. It also helps to confirm in your service agreement which controls you manage and which stay with the client. Have your own attorney review that wording, because shared responsibility gets fuzzy after a claim.
Turning Audit Readiness Into a Service That Pays
If you do all this for free, it becomes a hidden cost. Package it instead, and treat MSP compliance work as a product with a clear scope. Carriers may also ask about your own security as a provider, so keep your house in order too. Three simple offers cover most small-business clients:
- A one-time readiness review that produces the gap list and the first evidence pack
- An audit-ready managed plan with quarterly evidence refreshes and compliance reporting
- Renewal support that includes questionnaire review and broker coordination
The business logic is straightforward. Clients who buy readiness often end up buying the controls too, such as endpoint detection, MFA tooling, and tested backups. That lifts recurring revenue. They also leave less often, since you hold the paperwork that keeps their policy alive. Track the hours you spend per renewal before and after, and the time savings will make the pricing case for you.
Some owners will want the client-side view of this process. Share our guide on how to prepare for cyber insurance audits with them. If a client is still deciding whether to buy coverage at all, point them to our piece on cyber insurance for small business.
Frequently Asked Questions
What do cyber insurers check during an audit?
They usually check MFA, endpoint detection, backups, patching, email security, privileged access, and an incident response plan. Expect requests for proof, not just yes or no answers.
How early should an MSP start preparing a client?
About 90 days before renewal works well. That leaves time to fix gaps and refresh evidence without rushed spending.
Can an MSP be held responsible if a client fails an audit?
It depends on your contract and what you promised to manage. Spell out shared responsibilities in writing and have an attorney review the language.
Is MFA alone enough to pass a cyber insurance audit?
No. Insurers look at the full set of controls, so MFA must sit alongside monitored endpoint protection, tested backups, and a written response plan.
Do small clients really need endpoint detection and response?
Most carriers now ask about it, even for small firms. Basic antivirus alone often no longer satisfies the question.
Make Your Next Renewal Season the Calm One
Audit prep works best as a habit, not a rescue mission. Assess early, close the big gaps, keep the evidence fresh, and answer every question honestly. Do that, and your clients keep their coverage while you keep their trust and a healthier margin.
If practical IT business thinking is your thing, the Business Tech section has plenty more where this came from. Next up: how to price a managed security bundle so audit work never goes unpaid.
No Comment! Be the first one.